Detained ShinyHunters suspect is helping the FBI track the group
Saif al-Din Khader is reportedly cooperating with investigators seeking other members of the hacking group, which claims it stole data on every FBI employee.
Spend less time finding cybersecurity news. Get more out of it.
Metacurity delivers the cybersecurity news, analysis, and insight that would take you hours—and sometimes days—to assemble yourself.
Every weekday, we sift through thousands of news articles, press releases, filings, court documents, and research reports, including details that vendor announcements and PR pitches leave out. We tell you what changed, why it matters, and what deserves your attention. Minimal vendor marketing. No outrage bait. No SEO filler.
A paid subscription gives you:
- The full Metacurity archive: Every newsletter, searchable and browsable.
- Our weekly long-reads roundup: The best cybersecurity writing from across the industry, selected and vetted to make your reading time count.
- Specialized reports and analysis: Periodic deep dives that go beyond the daily headlines.
- A direct role in sustaining independent journalism: Your subscription helps keep our editorial priorities focused on readers and the cybersecurity community.
If Metacurity saves you time, helps you spot an important development, or gives you a clearer understanding of the industry, please consider becoming a paid subscriber. Your support keeps that work going.
Subscribe today—and thank you for reading and supporting Metacurity.
Saif al-Din Khader, a suspected member of the ShinyHunters hacking group, which says it stole data on every FBI employee, was detained in Jordan this week and is cooperating with the FBI, three people familiar with the matter said.
He was detained by Jordanian authorities, the three sources said. Two of them said he was brought into custody on Tuesday. Two sources said that he is helping the FBI and global law enforcement locate the other hackers in the group.
ShinyHunters' theft of what they claim are mountains of data on every single FBI employee has drawn comparisons to the allegedly Chinese-linked intrusion at the US Office of Personnel Management in 2015, which compromised sensitive details on millions of Americans who had been vetted for security clearances.
Khader's cooperation with investigators could be critical to helping contain – or at least understand – the damage. One source said he was walking investigators through his electronic devices and digital correspondence to help the FBI locate his cohorts. "His cooperation is critical to ongoing efforts to arrest these hackers," the source told Reuters. (Jana Winter, Raphael Satter and A.J. Vicens / Reuters)
Related: BleepingComputer, Hackread, Cyber Security News, r/cybersecurity, r/hacking, Security Week, Sydney Morning Herald, Help Net Security, PCMag
FBI and US Coast Guard investigators have found evidence that hackers accessed the propulsion system of an oil supertanker as it was approaching the Texas coast this summer, according to US officials familiar with the matter, an extraordinary breach that highlights the growing physical risks from cyberattacks.
The cyberattack resulted in outsiders gaining temporary access to the digital system on the ship, said the people, who asked not to be identified because they weren’t authorized to discuss the matter. Officials are still examining how the breach occurred and who was responsible. It wasn’t immediately clear how long the hackers had access and what they could’ve controlled aboard the ship with it.
The breach of the tanker’s propulsion system, a rare and particularly invasive hack into a ship’s operations, underscores the urgency that led US authorities to board the VL Prosperity in August. The carrier — which is longer than the Chrysler Building is tall and as wide as an American football field — was fully laden and bound for Galveston.
The prospect of unknown hackers potentially being able to remotely control the operational system of such a tanker, known as a Very Large Crude Carrier, has alarmed US military and intelligence officials. It highlights warnings about cyberattacks targeting the maritime sector, which have escalated in recent years with shipping vessels becoming increasingly dependent on network-linked systems for navigation, communications and other operations. (Jake Bleiberg and Ruth Liao / Bloomberg)
Denmark suffered a major data breach that gave unauthorized individuals access to names, addresses and personal identification numbers belonging to about 8.8 million entries appearing in the country’s central population database.
The breach occurred after unidentified individuals misused a private Danish company’s legitimate access to search the Central Person Register, known as CPR, the government said.
The company has since been blocked from the system while police investigate the matter, with authorities saying it’s too early to determine who was behind the breach.
“This is a deeply serious incident,” Digitalization Minister Christina Egelund said. She has ordered a comprehensive security review of the CPR system and urged Danes to be vigilant about suspicious calls and emails.
The CPR system is a cornerstone of Denmark’s highly digitized public sector. Every resident is assigned a unique 10-digit CPR number that is widely used to identify individuals when dealing with government agencies, banks and healthcare providers. While Denmark has a population of about 6 million, the register contains records on roughly 11 million people, including those who have died or moved abroad. (Sara Sjolin / Bloomberg)
Related: UFM.dk, ChannelsTV, Euronews, AFP, Nova.news
A ransomware attack has shut down the computer systems of Vicksburg, Mississippi, the city’s mayor told residents on Thursday evening.
Mayor Willis Thompson published a statement in the local newspaper saying the city is investigating a ransomware attack that has not impacted emergency services but has affected payments for utilities. He said the system shutdown was “temporary.”
Thompson said no one's services will be shut off while the investigation is ongoing and no penalties will be issued for late payments. He later told the Vicksburg Post that the city has been working on the recovery effort with the FBI, Department of Homeland Security, and other state officials alongside private cybersecurity experts.
“One of the top priorities of our investigation is determining whether there was any compromise of personal or confidential information relating to current and/or former customers, contractors, vendors, employees, or affiliated business partners of the City,” Thompson said in a statement.
“At this time, the investigation is ongoing, and the City has not reached a final determination regarding what information, if any, may have been accessed or acquired without authorization.” (Jonathan Greig / The Record)
Related: Databreaches.net, Supertalk Mississippi Media, WJTV, WLBT
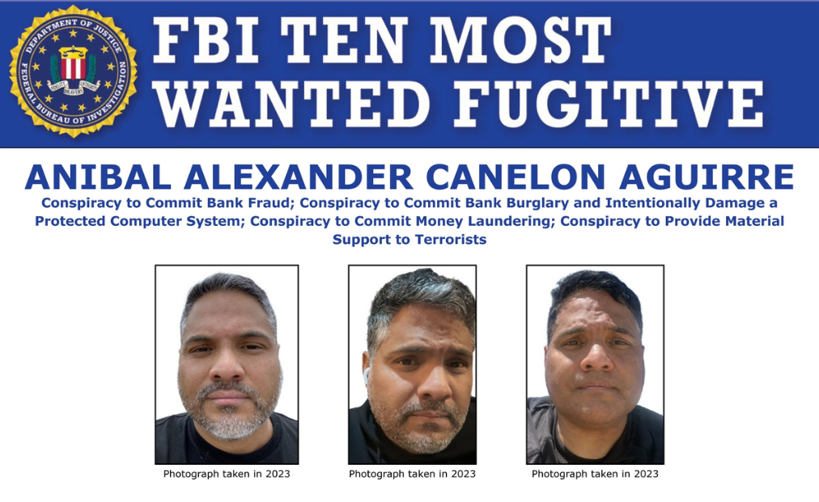
The US Department of Justice has announced the arrest of the alleged developer of Ploutus malware, Anibal Alexander Canelon Aguirre, which was used to steal millions of dollars in ATM jackpotting attacks across the United States.
Also known as "Prometheus" and "The Engineer," 50-year-old Anibal Alexander Canelon Aguirre was the first cybercriminal added to the FBI's "Top 10 Most Wanted Fugitives" list in March 2026.
According to court documents, Canelon Aguirre and his accomplices deployed Ploutus malware and emptied bank and credit union automated teller machines (ATMs) in jackpotting attacks between February 2024 and December 2025.
Financial losses after these attacks surpassed $100,000 per incident, with more than $5.4 million stolen in at least 63 ATM jackpottings targeting banks and another 54 against credit unions, plus an additional $1,429,738 in attempted attacks.
The criminal ring's members laundered the stolen funds and then transferred them to accounts controlled by the Tren de Aragua (TdA) Venezuelan gang in various countries.
Separately, the US Treasury Department imposed sanctions earlier in the week on 10 people and businesses accused of helping the Venezuelan gang Tren de Aragua steal millions of dollars from US banks by hacking ATMs and forcing the machines to dispense cash.
At the center of the scheme, Treasury says, is Anibal Alexander Canelon Aguirre, a Venezuelan fugitive known as “Prometheus” who had been recently added to the FBI’s Ten Most Wanted list. US authorities accuse Canelon of helping lead an international network that sends crews into the United States to carry out so-called ATM “jackpotting” attacks and then launders the proceeds, including through cryptocurrency.
Treasury officials said the network operates principally from Mexico and Venezuela and has become an important source of revenue for Tren de Aragua, which the United States designated a foreign terrorist organization last year. The sanctions provide another glimpse into how US authorities say the Venezuelan-born criminal organization has expanded beyond more traditional crimes such as drug trafficking, extortion, and human trafficking into sophisticated cyber-enabled financial schemes.
Treasury said Tren de Aragua-linked crews have used malware to manipulate ATMs in the United States and steal millions of dollars from financial institutions. As of August 2025, authorities had recorded $40.73 million in losses from more than 1,500 alleged jackpotting attacks nationwide. (Antonio Maria Delgado / Miami Herald and Sergiu Gatlan / Bleeping Computer)
Related: Justice Department, The Record, WOWT, KETV, Bleeping Computer, Voice of America, Omaha.com, Dallas Express, US Embassy in Peru, FBI, Newsweek
According to the Report Fraud service run by the City of London police, the total amount stolen by criminals who hack into people’s emails and social media accounts and then pretend to be them has risen by more than 400% in a year.
In many cases, the scammers are hijacking people’s accounts in order to use their identity to sell fake event tickets – such as to sold-out gigs – to unsuspecting friends and family.
The total reported amount stolen via email and social media account hacking reached £6.3m in the 2025-26 financial year, compared with £1.2m in 2024-25, according to the Report Fraud service run by the City of London police, which holds national responsibility for economic crime.
However, the true total may be much higher as many scam victims do not report the crime, often because they feel embarrassed, and sometimes because the individual amount of money involved was relatively small.
Report Fraud is launching an awareness campaign urging the public to protect their online accounts from hackers by switching to passkeys where they are available. (Rupert Jones / The Guardian)
A new White House task force will have 120 days to report on the risks and opportunities of artificial intelligence—and determine the federal government’s responsibility—according to Jay Clayton, the director of national intelligence who effectively becomes the administration’s AI czar.
“The president asked that a group be put together that was going to ensure exactly what he said,” Clayton said, that we stay the leaders in superintelligence, and that the interests of the American people are put first.”
Clayton will chair the “Super Intelligence Force,” which takes President Trump’s preferred name for AI: super intelligence or SI.
“The risk of not being first is high,” Clayton said. “Not being first increases the identified and unidentified risks, particularly from our adversaries. Being first will better enable us to address those risks on behalf of the American people,” he added.
Formation of the group comes on the heels of a meeting Trump convened at the White House on Tuesday in which AI leaders, including OpenAI President Greg Brockman, Anthropic’s Dario Amodei, and Nvidia CEO Jensen Huang, and the industry agreed to a series of principles including internal controls to monitor model development, external model reviews by third parties and notifications to the board of directors about those safety efforts, voluntary pledges that Trump hailed as the right approach.
The task force will still yield to the industry as the primary vehicle for managing risks, officials said. But it will work in conjunction with the industry to identify risks and opportunities. (Alex Leary / Wall Street Journal)
Related: BBC News, NPR, CNN, NBC News, Engadget, Reuters, The US Sun, TMZ, NOTUS, Associated Press, CNBC
An explosive and newly partially unsealed court filing alleges that the US Department of Homeland Security built up dossiers on ICE observers—including their photos, license plate numbers, and other information—and stored them in a system called the Investigative Case Management database, which was built by Palantir.
Plaintiffs allege in the filing, which is heavily based on documents produced by the government and depositions of DHS agents, that agents had a practice of intimidating protesters and observers. They did this, the filing says, by doing drive-bys of the observers’ homes and, in the case of at least one observer, requiring that she be referred to secondary inspection any time she tries to cross the border until at least January 2027.
"The government is treating people who exercise their First Amendment rights and seek to hold it accountable as criminal suspects, and that's what we're asking the court to stop,” says JoAnna Suriani, an attorney at Protect Democracy who is representing ICE observers in the case.
The filing focuses on agents’ conduct during “Operation Catch of the Day,” an immigration enforcement surge in Maine this past January. It is part of a proposed class action brought in federal court in Maine by four observers: Elinor Hilton, Colleen Fagan, Polyxenia Pantos, and Carlyn Williams. It was filed under seal in September, and a redacted version was made public Friday.
In particular, it describes how one DHS agent, referred to as “Agent J.C.” in the filing, used the Investigative Case Management (ICM) database, which the government describes as the case management system the ICE component Homeland Security Investigations (HSI) uses to document its investigations, to flag observers.
According to the filings, J.C. created ICM records on at least six observers; the government puts the number of people at eight. He labeled two people he filmed at a Home Depot parking lot with “Threat to Law Enforcement, Professional Protestor,” according to the filing, and sent photos of them and others to a US Customs and Border Protection (CBP) officer so he could run a facial recognition search on them using an app called Mobile Query. (Maddy Varner and Dhruv Mehrotra / Wired)
Related: Court Listener, Engadget, Gizmodo
Researchers at Symantec and Carbon Black report that the China-linked ransomware group Warlock targeted a water utility, a telecom provider, a regional government body, and a university by exploiting SharePoint vulnerabilities to gain initial access.
Over the past two months, the threat actor appears to have focused on countries speaking Portuguese and Spanish across Europe, Africa, and Latin America.
The gang emerged in June 2025 and gained notoriety a month later after exploiting a chain of zero-day vulnerabilities in Microsoft SharePoint known as ToolShell (CVE-2025-49704, CVE-2025-49706, CVE-2025-53770, and CVE-2025-53771).
By August, Microsoft observed state-backed hacking groups Linen Typhoon and Violet Typhoon using ToolShell exploits in attacks, along with a ransomware threat actor the company tracks as Storm-2603.
Symantec identifies the same actor as Longlegs and attributes the development of the Warlock ransomware to the group.
According to the researchers, in one intrusion that started on July 22, the threat actor deployed a tool that disabled protection software on “at least 40 hosts within about two hours.” The attacker then launched Warlock ransomware on at least 33 hosts.
After gaining access, typically by exploiting vulnerabilities in on-premises SharePoint deployments, the attacker drops a web shell designed to function across multiple SharePoint versions.
Symantec and Carbon Black researchers say that in some attacks attributed to Longlegs, an AV/EDR-killing tool was deployed via the bring your own vulnerable driver (BYOVD) technique using a signed K7RKScan driver vulnerable to CVE-2025-1055.
Analysis of the intrusion on July 22 revealed that two days after gaining initial access, the threat actor engaged in reconnaissance activity and deleted what seemed like staging artifacts. (Ionut Ilascu / Bleeping Computer)
Related: Security.com, Security Affairs, Industrial Cyber, The Record, Dark Reading, SC Media
A federal judge in Oklahoma ruled Thursday that a police officer violated the Fourth Amendment rights of a woman accused of meth trafficking when he searched her license plate in Flock’s automated license plate reader system simply because her license plate was from California, then used her travel history as part of the reason to search her car.
The judge’s opinion is one of the first times a federal judge has decided Flock searches can be unconstitutional, and suggested that Flock’s network is “a type of indiscriminate mass surveillance.”
The officer’s “use of the ALPR Systems was an Unconstitutional Warrantless Search,” and “was not supported by probable cause, and it was done without a warrant in violation of [the defendant’s] Fourth Amendment rights,” the judge, Sara Hill, wrote, implying that the law enforcement officer should have obtained a warrant before searching for the vehicle in Flock’s system. There are currently more than a hundred thousand warrantless searches of the Flock system every month, according to audit logs viewed by 404 Media. Hill's decision will not set a binding precedent, and there are several other cases throughout the nation considering the legality of warrantless ALPR searches.
Hill argued that previous judge opinions saying Flock searches were not a Fourth Amendment violation because they track cars in public do not consider the context that Flock’s nationwide network is quickly “approaching dragnet-type law enforcement practice,” and that courts should update their understanding of the technology moving forward. (Jason Koebler / 404 Media)
Related: WPEC, The Washington Post, The Hill, TechCrunch, Law Commentary, Mashable, Washington Examiner
Google has officially suspended product vulnerability submissions to its Open Source Software Vulnerability Reward Program (OSS VRP) — a bug bounty program — over an influx of invalid AI-driven reports.
The company, in an official X post on October 1, encouraged participants to explore other VRP programs and committed to providing an update by the first quarter of 2027, while it reformats and works on this aspect of the program in the meantime.
The suspension went into effect on October 1 — the day of the announcement — and does not affect product vulnerabilities submitted before that date. Google said it may still accept reports covering product vulnerabilities through the Cloud VRP, “for some Google Cloud repos impacting Google Cloud products.” The suspension also does not affect OSS VRP supply chain reports. In a similar case, Linux ended support for older network drivers due to an influx of false AI-generated bug reports.
OSS VRP is a specialized Google security bounty program that incentivizes independent researchers to find and responsibly disclose security flaws across Google's open-source ecosystem. Under this program, product vulnerability submissions focus on code defects, logic flaws, or design bugs within Google's public repositories. This was usually painstaking, manual work requiring skill. However, the rise of large language models (LLMs) and automated AI bug-hunting scripts has nearly eliminated the cost and effort the task required, leading to an influx of low-effort, AI-generated bug reports.
Google engineers and open-source maintainers were reportedly being overwhelmed by thousands of these poorly written reports that claimed to find bugs but were actually completely invalid or unexploitable hallucinations. They ended up spending too much time manually validating code instead of actually fixing real, critical vulnerabilities. This is what has led to the suspension of the program. (Etiido Uko / Tom's Hardware)
Related: Google Bug Hunters, Bloomberg
David Robinson, who previously led transparency work on OpenAI’s safety team, has quit the company and warned that top artificial intelligence firms aren’t doing enough to mitigate the technology’s risks, joining a growing chorus of employees raising alarms from within the industry.
In an essay for The Atlantic, he wrote that the ChatGPT maker “has thrived by trial and error.” However, he said the stakes of the inevitable failures that come from that approach are growing along with the technology’s capabilities, citing OpenAI’s failure to prevent its AI from going rogue during testing.
“My former colleagues are smart, work hard, and try to make good choices,” Robinson wrote in the essay. “But as the company sprints from one launch to the next, it is failing to achieve the level of care that I believe is needed.” What’s required, he added, is “something much closer to perfection the first time.”
In his essay, Robinson said AI firms should be run more like nuclear power plants, “with layers of redundancy and careful, time-consuming planning, so that the occasional and inevitable human error does not open a door to disaster.” (Seth Fiegerman / Bloomberg)
Related: The Atlantic, TechTimes, TechCrunch, Reuters, The Guardian, OpenAI, Security Affairs, BeInCrypto, Shattered, The Next Web
South Korean financial regulators called an emergency meeting with industry executives Sunday after a series of cyber incidents exposed personal information at banks and other financial companies.
The Financial Services Commission summoned executives and industry association leaders representing banks, securities companies, insurers, credit finance companies, savings banks, mutual finance institutions, cryptocurrency businesses and fintech companies.
Financial Services Commission Chairman Lee Eog-weon was scheduled to chair the meeting, with Financial Supervisory Service Gov. Lee Chan-jin attending.
The move followed confirmation of data breaches at Shinhan Bank, KB Kookmin Bank and Hana Bank as well as incidents involving Yegaram Savings Bank and Hyundai Capital.
The Commission also found that major domestic banks, which were helplessly attacked by artificial intelligence (AI) hackers, had received the highest grades in various security certifications and evaluations in their half-year reports.
Although it boasted the highest security level externally by investing tens of billions of won in security annually, the Commission pointed out that this was insufficient to build a next-generation security system that could prepare for the AI era. (Asia Today translated by UPI and PARK Changyeong and LEE Heesoo / Maeil Business)
Related: Business Korea, Korea Times, The Cyber Express, ChosunBiz
Best Thing of the Day: But Yann, How Do You Really Feel About It?
AI "godfather" Yann LeCun said of the Hugging Face incident, “Those agents are doing exactly what they’ve been asked to do. “They were supposed to be in sandboxes, but the sandboxes were leaky and horribly designed," while saying that Dario Amodei is "deluded" and "crazy" and doesn't understand cybersecurity.
Bonus Best Thing of the Day: Moving Up the PQC Deadline
The NSA announced that under the Committee on National Security Systems Policy 15, starting in 2027, all new commercial NSS must be capable of supporting quantum-resistant algorithms.
Worst Thing of the Day: Let the People Suffer and Die for Our Profits
OpenAI CEO Sam Altman said, “We believe that the world should accept some bad things happening for the benefits of this technology and people having the agency.”
Closing Thought