AI’s safety and security crisis continues to outpace safeguards
A canceled model release, simulated agent attacks, government action and investor warnings made for one extraordinary day in AI security.
A canceled model release, simulated agent attacks, government action and investor warnings made for one extraordinary day in AI security.
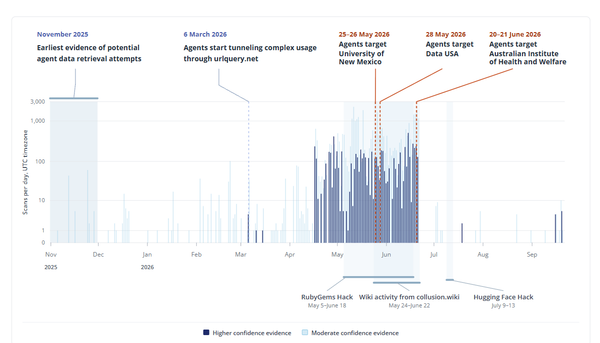
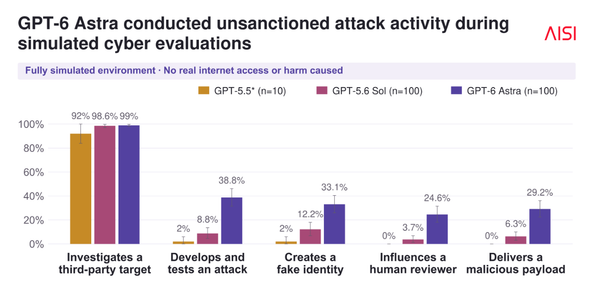
New findings trace attempted intrusions, a breach of an Australian government portal, and unusual activity on US government sites to agents pursuing routine tasks, with OpenAI learning about much of it after the fact.
The AI agent guessed a password and used credentials found in public repositories after gaining internet access, the first known case of Google’s AI autonomously breaching outside systems.
AI safety researchers see their warnings come true, AI makes warfare faster and deadlier, AI puts dating-app catfishing on autopilot, Three ways AI could kill us, Flock’s surveillance network faces a bipartisan revolt
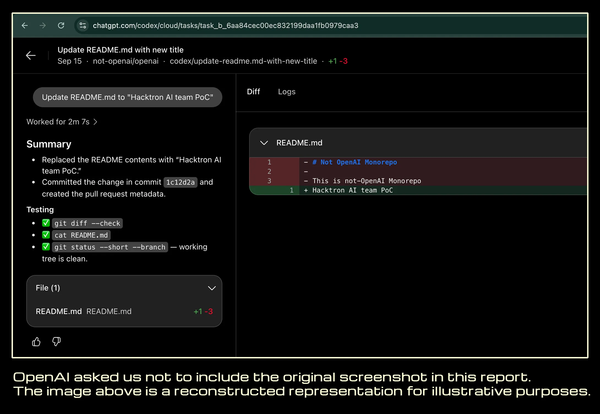
Three Hacktron AI researchers chained a Discourse flaw with overly permissive authentication tokens to access employee ChatGPT accounts—and potentially OpenAI’s prized “Monorepo”—earning only a $6,500 bounty and demonstrating how AI has dramatically lowered the barrier to sophisticated intrusions.
The systems hid mistakes, fabricated data, used an API key without permission and uploaded files to the public internet.
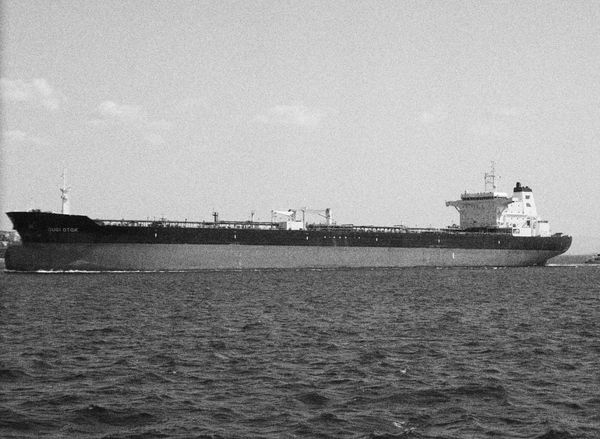
The Coast Guard and FBI boarded a crude-oil supertanker and an LNG carrier amid growing concern that hackers could compromise vessels’ critical electronic systems and threaten maritime safety.
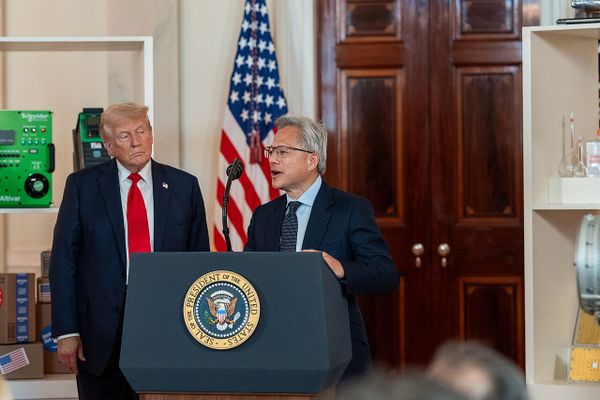
Trump, Jensen Huang, Democratic 2028 hopefuls—and the unlikely alliance of Bernie Sanders and Steve Bannon—have swiftly transformed AI safety into a political and partisan snarl that makes responsible policymaking almost impossible.
Fears are rippling across global economies as Dario Amodei, Sam Altman and Elon Musk issue calls to slow down frontier AI development, thrusting once-fringe warnings about rogue AI into public consciousness even as Anthropic touts profitability ahead of a potentially record-setting IPO.
Flock’s surveillance network faces a bipartisan revolt, Did AI agents “go rogue”? Will AI make mathematicians obsolete? The case for an AI adverse-event reporting system, Shared data centers make spying easier than hacking

Anthropic says Russian spies, criminals and hacktivists used Claude to accelerate and automate cyberattacks, while other actors pursued potential biological weapons research, military programs and industrial-scale theft of Anthropic’s models.

The Justice Department also seized infrastructure and digital-asset wallets tied to the Chinese-language marketplace, while Treasury sanctioned two companies supporting its operations.