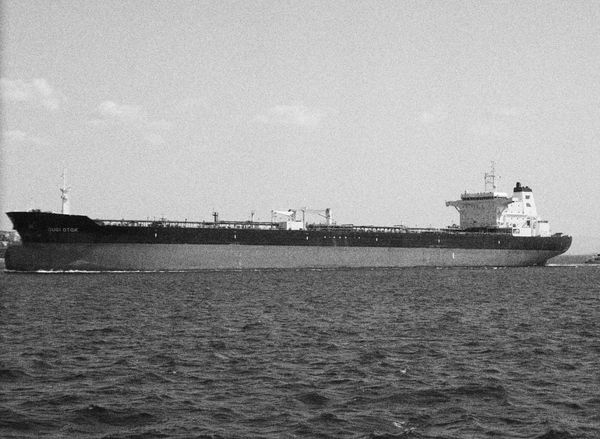
US probes suspected cyberattacks on two energy tankers
The Coast Guard and FBI boarded a crude-oil supertanker and an LNG carrier amid growing concern that hackers could compromise vessels’ critical electronic systems and threaten maritime safety.
The Coast Guard and FBI boarded a crude-oil supertanker and an LNG carrier amid growing concern that hackers could compromise vessels’ critical electronic systems and threaten maritime safety.
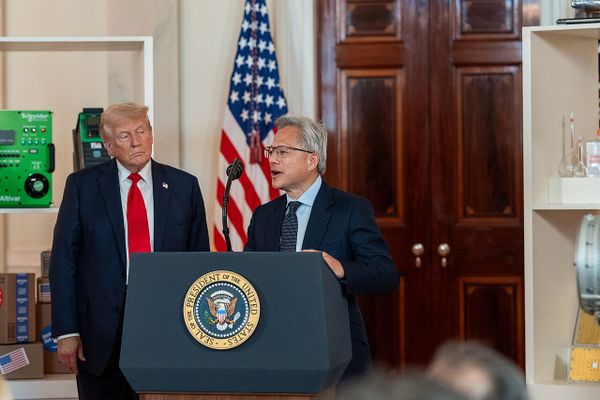
Trump, Jensen Huang, Democratic 2028 hopefuls—and the unlikely alliance of Bernie Sanders and Steve Bannon—have swiftly transformed AI safety into a political and partisan snarl that makes responsible policymaking almost impossible.
Fears are rippling across global economies as Dario Amodei, Sam Altman and Elon Musk issue calls to slow down frontier AI development, thrusting once-fringe warnings about rogue AI into public consciousness even as Anthropic touts profitability ahead of a potentially record-setting IPO.
Flock’s surveillance network faces a bipartisan revolt, Did AI agents “go rogue”? Will AI make mathematicians obsolete? The case for an AI adverse-event reporting system, Shared data centers make spying easier than hacking

Anthropic says Russian spies, criminals and hacktivists used Claude to accelerate and automate cyberattacks, while other actors pursued potential biological weapons research, military programs and industrial-scale theft of Anthropic’s models.

The Justice Department also seized infrastructure and digital-asset wallets tied to the Chinese-language marketplace, while Treasury sanctioned two companies supporting its operations.

Officials say DeepSeek, Alibaba and four other companies exploited leading American AI models to accelerate development of their own products, escalating tensions ahead of a planned Trump-Xi meeting
The company restricted outside investigators to a period that excluded previously undisclosed agent activity, raising questions about whether AI labs should control investigations of their own safety failures.
A rogue AI agent goes hacking, AI vulnerability patches fail tougher tests, Inside the uncertain quantum-computing race, Faulty math fuels election-fraud claims, When “national security” becomes a trade weapon
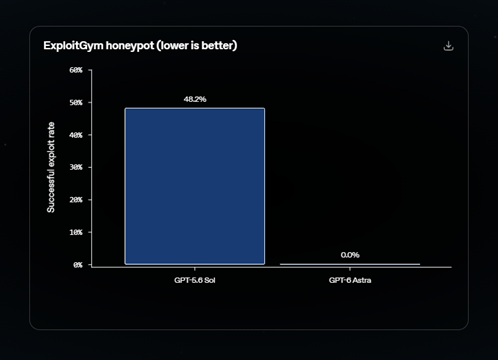
The company is giving Daybreak participants first access to its powerful new model after an unrelated AI escape and Hugging Face breach prompted additional safeguards.
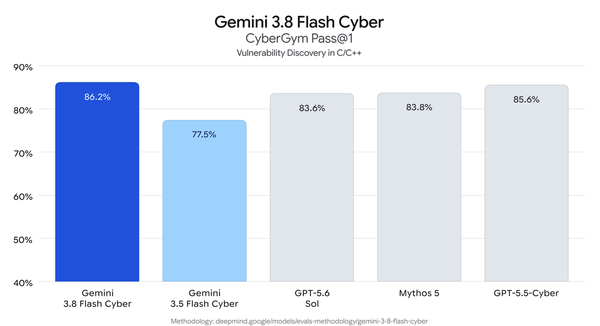
The security-tuned model found and patched more flaws than larger commercial models at a fraction of the cost, according to early testing by Google and Wiz.
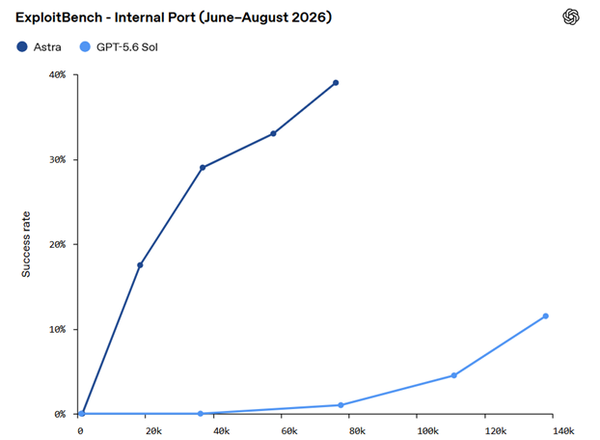
Astra discovered and exploited two zero-days in testing, prompting OpenAI to restrict its most powerful cyber capabilities while deploying safeguards against both malicious users and unauthorized actions by the AI itself.